MISSION CRITICAL
VISITOR INTEL
Built for Facility Security Officers (FSOs) who demand audit-ready evidence, not just visitor logs. SecurePoint USA operationalizes ITAR/EAR compliance at the speed of defense.
Paper Logs are an
Audit Liability.
When DCMA shows up, "I think we screened them" isn’t a strategy. You need current-list screening, append-only records, and evidence packs that survive federal review.
No Proof of Screening
Manual OFAC/BIS checks are hard to document. If you can't prove you screened them, it didn't happen.
Incomplete Audit Trails
Visitor logs without technical data access links force FSOs to cross-reference multiple failed systems.
Data Silos
Lobby checks that don't flow into your compliance engine create huge visibility gaps during DCSA reviews.
Defense-Grade
Intelligence
We don’t just check visitors in. We integrate visitor identity with your global compliance obligations. From real-time sanctions screening to technical data access reporting.
Checksummed Evidence Packs
One-click exports for DCMA/DCSA audits. Cryptographically hashed records that help prove screening occurred.
Unlimited Sanctions Screening
Screen every guest across OFAC, BIS, UN, EU, and UK lists with zero per-check fees.
After Visit Reporting
Hosts log meeting outcomes and technical exchanges, directly linking visits to export controls.
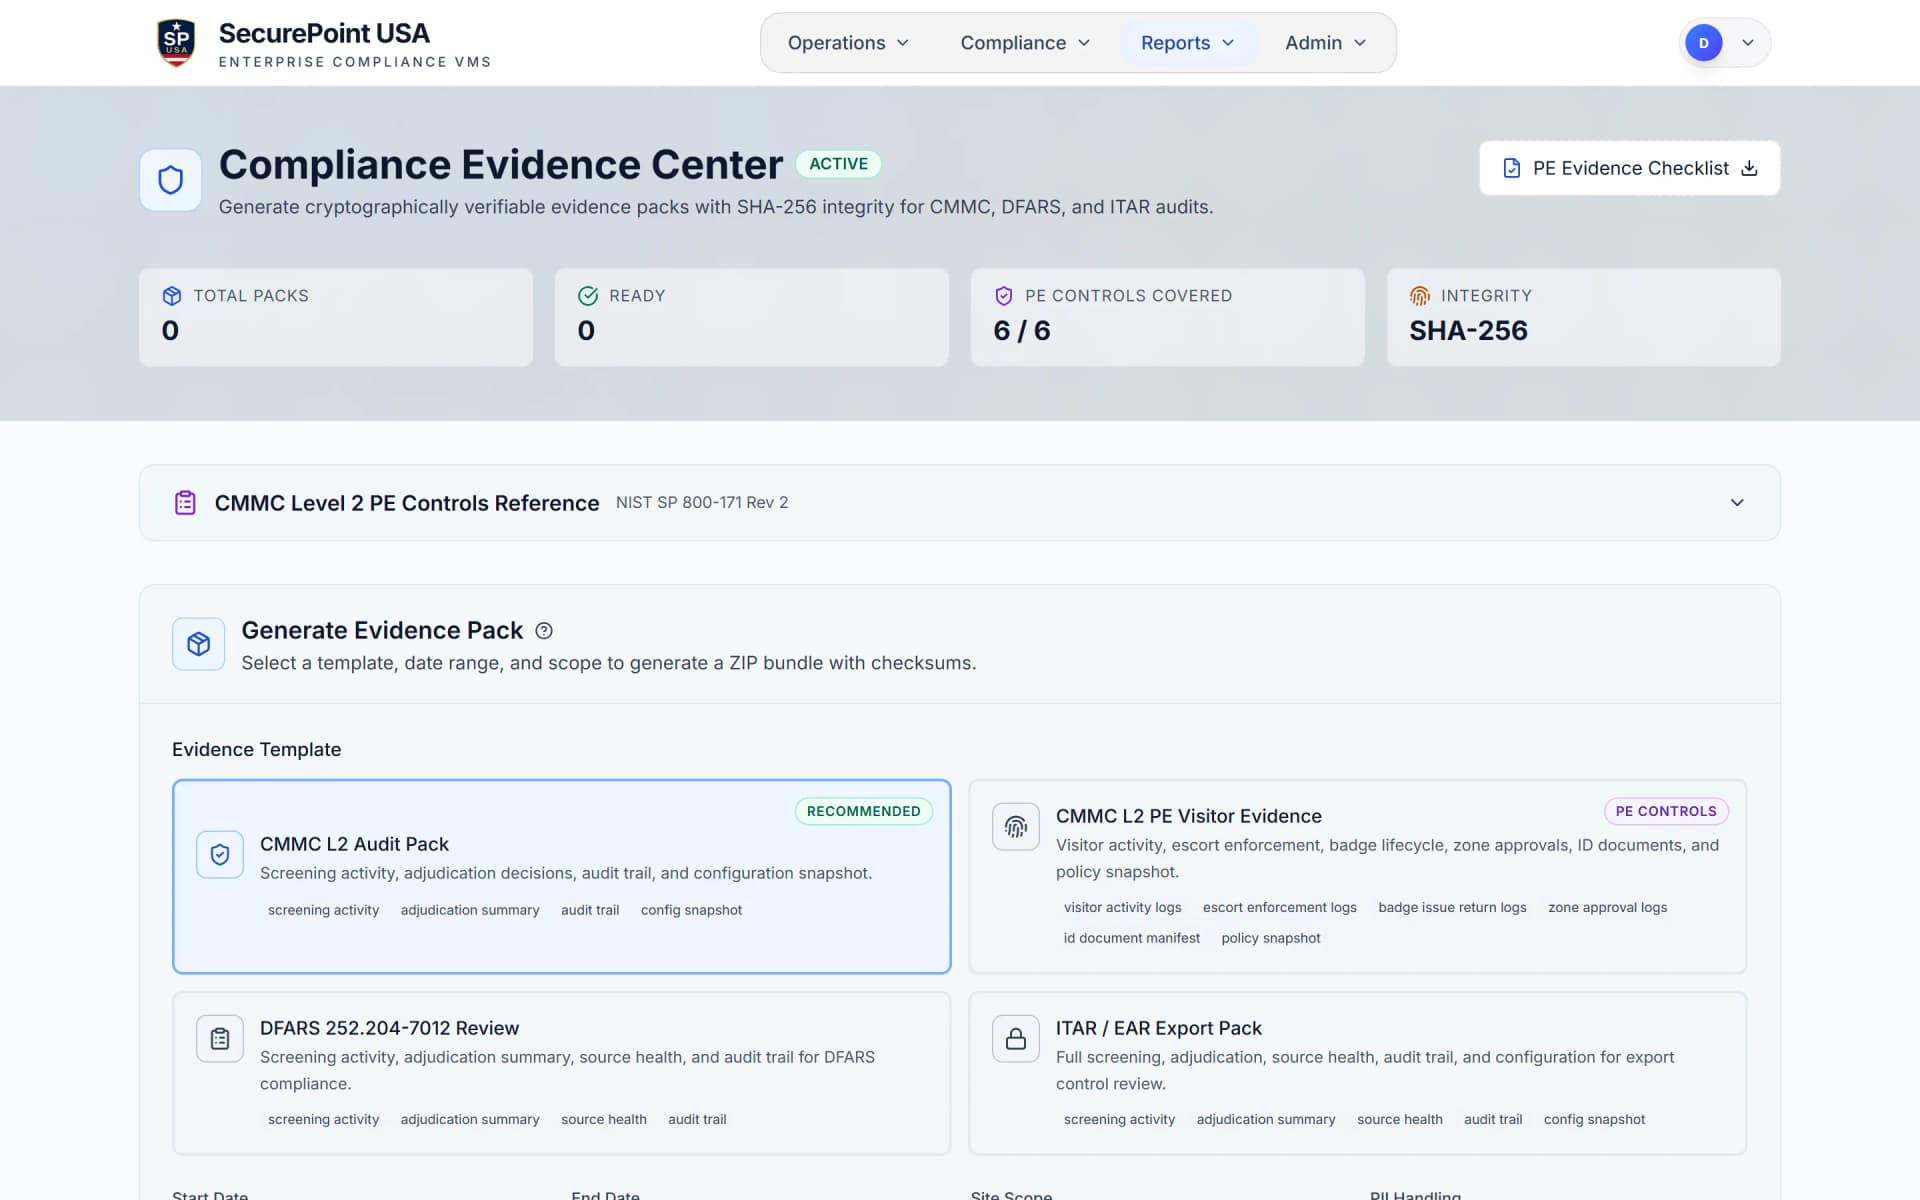
Evidence packs tie visitor sessions, screening results, approvals, and reviewer rationale into one exportable record for compliance review.


Architected for
Compliance Enforcement
Data Integrity
Every log entry is hash-chained, so a verifier can detect tampering in the evidence presented to auditors.
Regulatory Mapping
Workflows are designed to support ITAR, EAR, CMMC, and DFARS visitor-control evidence needs.
Global Verification
Orchestrated screening across enabled sanctions lists with automated phonetic name matching and human review.
Intelligence
Briefing
Stay updated on the evolving landscape of defense compliance, ITAR regulations, and facility security protocols.

READY FOR
DEFENSE
WORKFLOWS
Pilot-ready for multi-site defense environments with front desk, host, and compliance workflows.
SecurePoint USA supports customer compliance workflows for ITAR, EAR, NIST SP 800-171, and CMMC requirements. We do not imply government certification or endorsement.
SecurePoint USA LLC is a U.S. company and is not affiliated with Securepoint GmbH or other vendors named Securepoint.
Frequently asked questions
Does SecurePoint make our facility ITAR compliant?
No. ITAR compliance is a program your organization runs, and the obligation stays with you. SecurePoint is a control inside that program: it screens visitors, captures purpose and host, records escort requirements, and keeps an audit trail of who entered and who permitted them.
What is a deemed export in a visitor context?
Releasing controlled technical data to a foreign person inside the United States can constitute an export under the ITAR and the EAR, including through a facility visit that gives access to controlled areas or data. Whether a specific release requires authorization is a determination for your export-control officer or counsel.
Can a visitor system replace our Technology Control Plan?
No. The Technology Control Plan is the document that defines your rules. A visitor system is one of the controls that carries those rules out at the door and records that they were applied. The plan stays yours to write, maintain and defend.
What gets recorded for a visit to a controlled area?
The visitor and their host, the stated purpose, the site, the escort requirement, the screening outcome, any adjudication decision with the reviewer who made it, badge issuance, and check-out. Those go to an append-only audit trail and export as an evidence pack.
Does screening tell us whether a visitor needs a license?
No. Screening tells you whether a party matches a restricted-party list and routes possible matches to a documented human review. License determinations belong with your export-control officer or trade counsel.