Blog
ITAR Visitor Management for Small Manufacturers: Your First System
A practical buying and setup guide for small defense suppliers, machine shops, and startups with one or two locations.
11 min readBy SecurePoint USA
Your shop may have one building, a small team, and only a few visitors each week. When a customer, calibration technician, or outside contractor arrives, someone still needs to own the visit.
Who is meeting them? Where may they go? What happens if screening needs review? And can you retrieve the record later?
A visitor management system is the software, usually with a tablet and a badge printer, that registers visitors, checks them in and keeps a record of each visit. This guide covers a practical first visitor management system (VMS) for small ITAR manufacturers and defense startups: the people, equipment, and decisions it takes to run one.
If you started with a paper sign-in book, that was a reasonable choice. The question now is whether it still runs the same way every time.
A few visitors still need a repeatable process
It is a fair question: why pay for software when only a handful of people visit each month?
Because every visit needs the same steps, and rare tasks are the easiest to get wrong. Someone has to expect the visitor, screen them, decide where they may go, and note when they left. In a small shop, the person who answers the door is often running a machine or on a customer call, so the steps depend on who happens to be free.
Then there is the record. The sign-in book holds a name and a time, the reason for the visit sits in someone’s email, and the escort sits in someone’s memory. Ask about a visit from last spring and someone rebuilds it from three places.
Visitor volume affects your budget and staffing. It does not change what a visitor may see or receive: one visitor who walks past an uncovered drawing raises the same question as fifty.
What the rules ask, briefly
A few legal points shape what your system needs to do.
- Showing can be exporting. Under the ITAR, releasing technical data to a foreign person in the United States is a deemed export (22 CFR 120.50). Release includes a visual inspection of a defense article that reveals technical data, and oral or written exchanges (22 CFR 120.56).
- U.S. person is broader than citizen. It also covers lawful permanent residents, certain protected individuals such as refugees and asylees, and U.S. companies (22 CFR 120.62).
- Four questions stay separate: who the person is, whether they are a U.S. person, whether screening cleared, and whether they may receive the specific information on this visit. A clean screen, NDA, badge or escort does not authorize a release that otherwise needs DDTC authorization.
- Paper is not illegal, and software is not compliance. NIST SP 800-171 Revision 2 says physical-access logs can be written, automated or a mix (requirement 3.10.4). NIST has since published Revision 3; your contract says which applies.
- Guidance is not a universal rule. DDTC’s ITAR Compliance Program Guidelines recommend elements such as physical security and records of foreign-person visits.
These rules turn on what a visitor could see or receive, not on nationality alone. A blanket ban on non-citizens can create its own legal problems, especially for job candidates. Our guides to ITAR visitor requirements and CMMC visitor log requirements go deeper.
Assign the people before you choose the tablet
A VMS works when four jobs have names next to them. Existing staff can cover all four where your policy permits.
- Process owner
- Sets up the system, keeps the visitor rules current, and fields problems.
- Backup
- Covers when the owner is out, with the same access and training.
- Visit host
- Meets the visitor, escorts them where your policy requires, and ends the visit.
- Authorized reviewer
- Resolves possible screening matches and access questions. Often an owner or officer, with export counsel on call.
An illustrative example, not a real customer: in a 20-person machine shop, the office manager owns the process, the quality manager is the backup, engineers host their own visitors, and the general manager reviews holds. No security department required.
Also decide where visitors wait, which areas are controlled (anywhere a visitor could see controlled drawings, parts or screens), and who to call when the reviewer is unreachable.
A self-service kiosk collects details, runs checks and records what happened. It does not decide who may see controlled data, and it does not replace an escort where one is required.
What your first system should support
Whatever product you choose, look for:
- Expected visitors and walk-ins: hosts register visitors ahead of time, and walk-ins follow a defined path.
- Screening against the restricted-party lists that matter to your business.
- A hold for unresolved results: a possible match, or a check that did not finish, waits for an authorized person.
- Required acknowledgements, such as an NDA or site rules, before the badge.
- Badge prerequisites: no badge until every required step is done.
- Checkout, so the record shows when the visitor left.
- Retrievable records of who visited, who hosted, what was checked and found, who decided and why, and what was signed. Ask how long ID images are kept, too; it is often shorter than the visit record.
What a held result means. The system cannot clear the visit on its own. Usually a name resembles a restricted-party list entry closely enough that a person should look, and most turn out to be different people. A hold is a pause, not an accusation. A check that could not finish should hold the visit too: no result is not a clean result.
How SecurePoint handles these today
- Screens against lists that include the OFAC SDN List, the BIS Entity List and the BIS Denied Persons List: walk-ins at check-in, preregistered visitors when they register and again at arrival unless a recent clearance for the same name still applies.
- Holds the visit and badge on a possible match, and treats a screen that cannot finish as a hold, never a pass. Only org admins and compliance managers can clear a hold.
- Blocks the badge until required steps such as an NDA or safety briefing are done. Staff can override some of those steps with a written reason, but never a screening hold.
- Records checkout at the kiosk or front desk. Visits left open close at the end of the day, flagged as a departure nobody observed.
- Protects visit records from deletion for ten years, with CSV and PDF reports and evidence packs for export.
- Does not verify identity, document authenticity or U.S.-person status. A visitor’s U.S.-person answer counts only when a host or staff member attests to it.
More on SecurePoint’s visitor management for ITAR facilities.
Five situations to test before you buy
Ask each vendor to run these live with test names, not real visitors, and treat every answer as unproven until you see it happen.
| Situation | Question to ask | Evidence to inspect |
|---|---|---|
| 1. A normal visit | Run a preregistered visit from arrival to checkout, then repeat it with a required acknowledgement unsigned. | Each step with its time, and who released the badge. With the acknowledgement missing, no badge unless someone authorized overrides it with a written reason. |
| 2. A walk-in whose host is out | Who is alerted, and who can take over the visit? | The alert, the handover, and the visitor waiting in reception, not let in. |
| 3. A possible restricted-party match | Use a test name that produces a possible match. Who can clear it? | The badge held, the review queue, and the reviewer’s decision and reason. Front-desk staff should not clear it alone. |
| 4. Screening that cannot finish | What happens if the screening service or the network is down? | The result shown as incomplete, never as clear, the badge held, and your written fallback. |
| 5. An older visit | Ask for a visit from several months ago. | How fast you find it, and whether it shows the host, checks, results, decisions, signatures and checkout, ready to export. |
In all five, look for the same outcome: no visit skips a required step unless a named person decides, and the record shows who.
A practical setup for your first location
For one location the list is short. The SecurePoint visitor hardware guide has current recommendations and how each was tested.
- Check-in device. The Samsung Galaxy Tab S10 FE, recommended first after SecurePoint’s own testing, or the Apple iPad 11-inch (A16). Both run the SecurePoint Kiosk app. Windows-only shops can use an Intel or AMD PC that prints through the SecurePoint Print Connector.
- Printer and labels. The Brother QL-820NWB with DK-2251 labels, the combination SecurePoint lists as supported.
- Stand. A locking stand made for your exact tablet, leaving the front camera and charging port open, angled away from glare.
- Network. Printer and tablet on the same network, the printer on Ethernet where you can. Guest Wi-Fi and separate VLANs usually block printing.
- A responsible person, usually the process owner, who keeps labels stocked and the tablet charged and running the app during visiting hours.
Already own a tablet or PC? Send SecurePoint the model before buying anything. Hardware prices change, so check current retail.
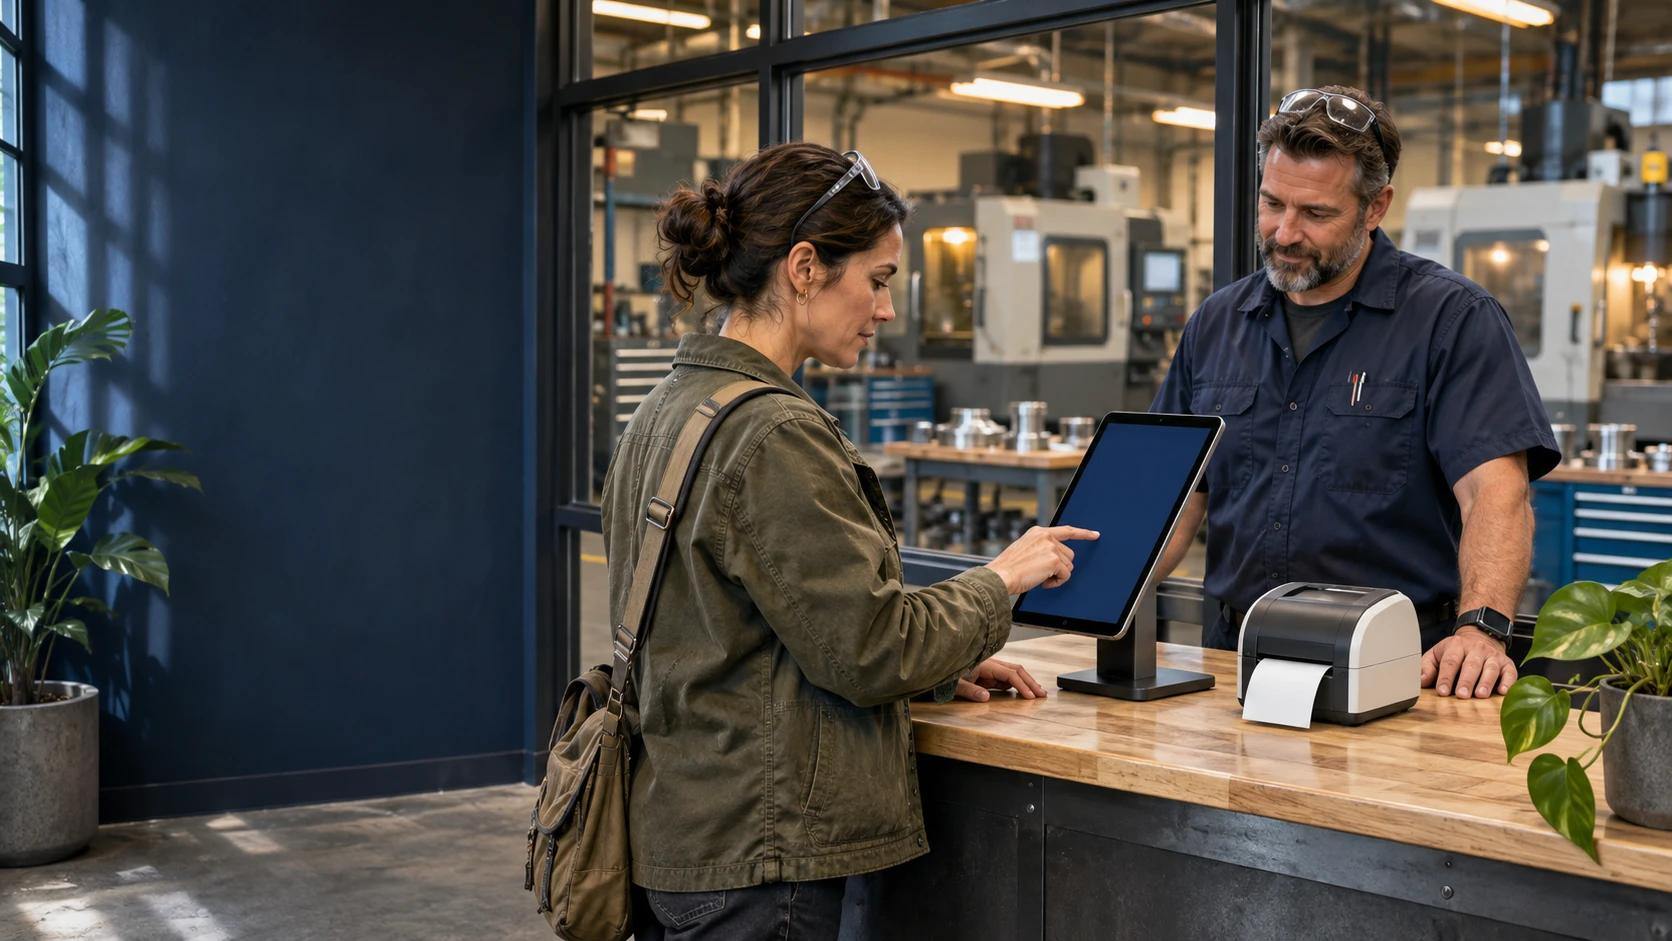
Where your site captures IDs, the kiosk also reads the details on the ID for the visitor to check, unless your organization turns that off. Neither the picture nor the reading verifies identity or establishes U.S.-person status. The scene at the top of this page is illustrative and does not show supported models.
What to budget for one location, then two
Prices are from the SecurePoint pricing page on November 20, 2026; check it for current figures.
- Software. Defense Front Desk, the plan with the ITAR and EAR workflow described here, is $249 per site per month billed annually ($2,988 a year) or $296 month-to-month. It includes ID capture, the NDA and safety briefing workflow, and badge design. The cheaper Starter plan leaves out the full ITAR and EAR workflow, so its price is not this setup’s.
- Hardware: a one-time purchase of tablet, stand and printer.
- Label supplies: an ongoing cost that grows with badges printed.
- Optional notifications: hosts get arrival alerts by email, and text-message alerts are a $29 per site per month add-on that each host opts into.
- Setup charges: the pricing page lists no setup fee; confirm it on your quote.
A second location adds a site, listed from $2,390 a year billed annually or $237 a month month-to-month on Defense Front Desk. It also needs its own station, printer and labels, a local owner and backup, and its own site settings. Add the lines up and ask for a written quote; hardware and add-ons vary too much for an all-in figure here.
Moving from paper to a working pilot
A suggested sequence, not a schedule; how long each step takes depends on your shop.
- Map the process and assign the four roles.
- Configure the first location: hosts, acknowledgements, screening and badges.
- Rehearse the five situations with test names.
- Train the owner and backup, then each host.
- Review the first weeks of records for skipped steps, unclear holds and missing checkouts.
- Add a second location once the first runs the same way every time.
Keep your paper books under your company’s retention policy. And write an outage procedure that keeps required checks in place: for example, visitors wait in reception until screening can run, and the owner notes what happened. No unscreened visitor enters a controlled area because a device was down.
Questions small manufacturers ask
We only get a few visitors a month. Do we need a visitor management system?
No rule requires software, and a paper process can work if it is followed every time. Low volume lowers your cost and staffing needs, not the care each visit needs.
Who runs it if we do not have a receptionist?
A named process owner and backup, with each host meeting, escorting where required, and checking out their own visitors. The kiosk records the steps; people decide holds and access.
Can we use a tablet or printer we already own?
Possibly. Confirm the model with the vendor before buying; SecurePoint supports the Brother QL-820NWB printer with DK-2251 labels.
Will a visitor management system make us ITAR compliant?
No. It is one control inside your compliance program. Decisions about who may receive controlled technical data, and under what authorization, stay with your company.
What changes when we add a second location?
Another site subscription and check-in station, a local owner and backup, and that site’s own settings. Rerun the five test situations there before relying on it.
Before you choose your first visitor system
- A named process owner, backup and authorized reviewer
- Hosts who know they meet, escort where required, and check out their visitors
- A visitor waiting area, a list of controlled areas, and an escalation contact
- The lists you screen against, and who decides possible matches
- Required acknowledgements and badge prerequisites, written down
- The five test situations, run live with each vendor
- Hardware compatibility confirmed before you buy
- A first-year budget: software, hardware, labels, add-ons and any setup fee
- A written outage procedure that keeps required checks in place
- Existing paper records kept under your retention policy
See how SecurePoint would work at your first location.
Walk through a normal check-in, a screening hold, and the visit record your team keeps afterward.
See the visitor workflowSources
- DDTC: ITAR Compliance Program Guidelines (PDF)
- 22 CFR 120.50, Export (eCFR)
- 22 CFR 120.56, Release (eCFR)
- 22 CFR 120.62, U.S. person (eCFR)
- NIST SP 800-171 Revision 2, requirement 3.10.4 (PDF). NIST has since published Revision 3.
This article describes regulations, guidance and product details as of November 20, 2026. What applies to you depends on your activities, the information involved, your authorizations and your contracts. SecurePoint supports compliance workflows; it does not provide legal advice or guarantee regulatory compliance. Final access and compliance decisions rest with the controlling organization.