
Sanctions
OFAC 50 Percent Rule for Visitor and Entity Screening
A practical guide to OFAC ownership aggregation, blocked entities, visitor screening workflows, and audit evidence for regulated facilities.
Oct 20, 2025
ReadBlog
On December 4, 2025, OFAC announced a $7M+ penalty against a company that ignored sanctions guidance around Russia-linked dealings. That fine is a flashing light for defense contractors and regulated manufacturers: one unvetted visitor, vendor, or field engineer can trigger the same chain reaction: audits, halted shipments, reputational damage, and consent orders. If OFAC or DCMA asked today, could you prove every visitor was screened against the latest lists, adjudicated by humans, and logged in an append-only audit log?
4 min readBy SecurePoint USA
What happened
OFAC cited repeated disregard for sanctions guidance: no real-time checks, weak ownership tracing, and missing controls. Defense contractors and ITAR/EAR programs face the same exposure: a visitor with a buried Russia ownership link walks in, and your program risk spikes. Documented controls, human review of possible matches, and a record of how each hit was resolved are the evidence you will want in hand.
Visitor flow risk
Sanctions risk isn't just for shipments. It shows up in lobby check-ins, contractor rotations, and vendor demos. A single miss can trigger ITAR/EAR disruptions or OFAC scrutiny.
SecurePoint controls
SecurePoint screens visitors against OFAC and BIS lists at check-in, holds possible matches for human review, and writes dispositions to an append-only audit log.
OFAC, BIS, UN, EU, UK with severity scoring. OFAC 50% ownership checks run in shadow mode by default, and BIS list matches go to a reviewer.
Possible matches go to a reviewer. Clean screens can auto-approve. Dispositions are logged.
Append-only logs: actor, org_id, action, target_id, metadata, timestamps. Built for regulator reviews.
Screening runs at check-in and on scheduled workforce and vendor re-screens, subject to the fair-use caps on each plan.
Red flags to catch
| Red Flag | Why It Matters | SecurePoint Control |
|---|---|---|
| Match on OFAC SDN or SSI | Strict liability. An SDN match is a stop point; SSI restrictions are narrower and depend on the directive. | Real-time SDN/SSI screening with severity labels and adjudication history. |
| Ownership link to sanctioned party (>50% aggregate) | OFAC 50% Rule aggregates blocked ownership, even if the entity is not listed. | Ownership look-through where ownership records exist. OFAC 50% results run in shadow mode by default. |
| Russia/Belarus nexus vendors or site access | Sectoral sanctions and export controls heighten risk for ITAR/EAR environments. | Screen against OFAC SDN/SSI and BIS lists, and hold elevated matches for human review. |
| Incomplete identity fields | Missing legal name or document capture weakens screening and the audit record. | Required identity fields and document capture at check-in before a badge can issue. |
| Ignored near-matches or repeat hits | Pattern of control failures; OFAC can weigh ignored warning signs as reckless conduct. | Hit history, reviewer notes, append-only audit logs, and escalation for high-severity hits. |
Illustrations
These are illustrations of adjudication, a review queue, and an enforcement cascade. They are not product screenshots.

Illustration of an adjudication drawer with a possible OFAC hit, match reasons, and review controls.

Illustration of a review queue with flagged visitors and list-source labels.

Illustration of how an OFAC penalty can cascade into paused shipments and a consent order.
10-minute hardening
Rapid actions to stay ahead of OFAC, ITAR/EAR, and BIS scrutiny while keeping throughput high.
Human-in-loop
AI is assistive, not determinative. Possible matches go to a reviewer. Clean screens can auto-approve.
See SecurePoint's real-time denied party screening, human-in-loop adjudication, and append-only audit trails in action. Keep screening inline without slowing your lobby.
Get occasional notes on sanctions, export controls, and visitor compliance when we publish them.
No spam. Unsubscribe anytime.
Related posts
More guidance on sanctions, export controls, and visitor management for regulated facilities.
A practical guide to OFAC ownership aggregation, blocked entities, visitor screening workflows, and audit evidence for regulated facilities.

New Treasury sanctions on a Caribbean narcotics network highlight hidden risks in global logistics and visitor management. Learn how to screen for these threats.
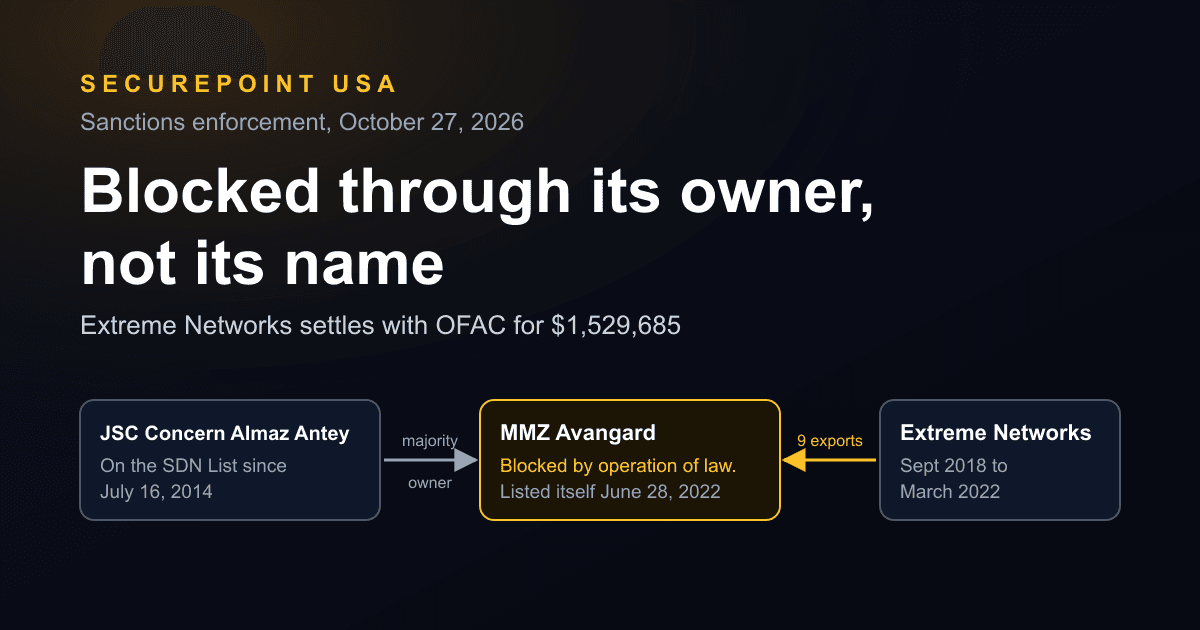
Extreme Networks settled with OFAC for $1,529,685 over nine exports to a Russian missile maker blocked through its owner. What ownership screening must cover.