The November 10 Double Deadline: CMMC Phase 2 and the BIS 50% Rule Land on the Same Day
Two rules, written by two different agencies for two unrelated reasons, were scheduled to hit the same people on the same date. Class Deviation 2026-O0025 suspended the CMMC Phase 2 C3PAO transition. The BIS Affiliates Rule was not part of that deviation: its one-year stay was set to end November 9, 2026, and its return on November 10 was never guaranteed. The panel below shows its status today.
Update: July 16, 2026
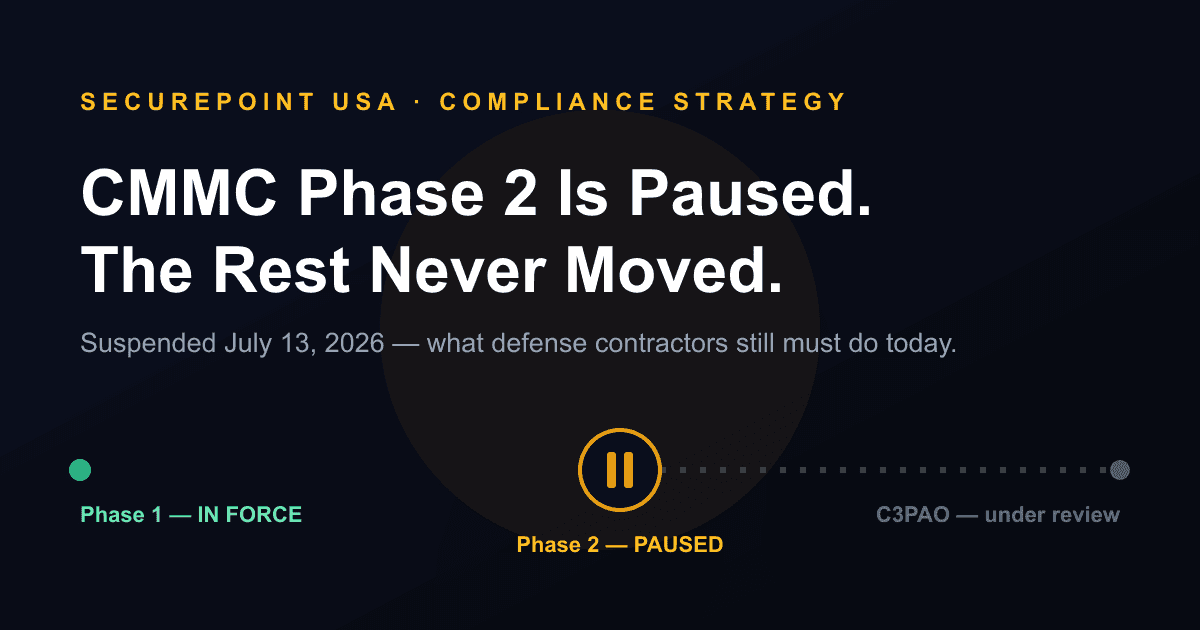
On July 13, 2026, the Department of War suspended CMMC Phase 2, the third-party (C3PAO) certification requirement described below, pending a 60-day program review. The November 10 Phase 2 transition is on hold, though DFARS 252.204-7012 and the Level 2 self-assessmentobligations remain fully in force. The BIS 50% Affiliates Rule discussion in this article is unaffected. See our current coverage: CMMC Phase 2 Is Paused, But the Requirements That Reach Your Front Desk Never Moved.
Most compliance crunches don't arrive as a single dramatic event. They arrive as a calendar collision: two obligations coming due in the same window, landing on the same small team. For the U.S. defense industrial base, that collision was scheduled for November 10, 2026. Half of it has already moved.
On that day, the cybersecurity rulebook and the export-control rulebook were scheduled to move at the same time. The Cybersecurity Maturity Model Certification (CMMC) program was to enter Phase 2, and the Bureau of Industry and Security's (BIS) “Affiliates Rule” (the 50% rule for export controls) was scheduled to come back into force after a one-year suspension. Class Deviation 2026-O0025 suspended the CMMC Phase 2 C3PAO transition. They have nothing to do with each other on paper. They still land on the same contractor, often the same person.
The short version
Class Deviation 2026-O0025 suspended the November 2026 C3PAO Level 2 transition; DFARS 252.204-7012 and Level 2 self-assessment remain in force. The same date was set for the BIS Affiliates Rule to extend export-control restrictions to companies that are 50%+ owned by listed parties. BIS has stayed it through November 9, 2026; treat November 10, 2026 as scheduled, not guaranteed.
Deadline one: CMMC Phase 2 is suspended
CMMC is how the Department of Defense verifies that contractors actually protect the government information they handle. The program is established under 32 CFR Part 170, and the contractual hook (the clause a contracting officer puts in a solicitation) is DFARS 252.204-7021. The acquisition rule that lets officers require a CMMC level took effect November 10, 2025, and the rollout is phased.
Phase 2 was to begin November 10, 2026. The change that would have mattered: for most contracts involving Controlled Unclassified Information (CUI), a Level 2 assessment by an accredited third party (a Certified Third-Party Assessment Organization, or C3PAO) would become a condition of award. Class Deviation 2026-O0025 suspended that transition. Self-assessment under DFARS 252.204-7012 remains in force. See our current coverage of the deviation.
The capacity math is the real deadline
DoD estimates roughly 80,000 contractors will ultimately need a Level 2 C3PAO certification. Yet the department's own rule projects assessment throughput ramping slowly: on the order of 135 assessments in year one, about 673 in year two, 2,252 in year three, and 4,452 in year four. A typical contractor needs 6–12 months just to become assessment-ready, and accredited assessors are finite. The queue, not the audit, is what catches people.
Here is where this stops being an IT problem. CMMC Level 2 is built on NIST SP 800-171, and one of its control families is Physical Protection (PE): escort and monitor visitors, maintain physical access logs, and control who can reach the systems and areas where CUI lives. Assessors do not accept “we have a policy.” They ask for the evidence. A spiral notebook at the front desk is one of the quiet places an otherwise-ready program loses points.
Where SecurePoint fits: our visitor platform generates time-stamped access logs, escort records, and an audit trail that support NIST 800-171 Physical Protection evidence. That is evidence for an assessor. It is not a CMMC certification.
Deadline two: the BIS 50% Rule makes ownership the new screen
The second clock is export controls. In September 2025, BIS published the Affiliates Rule (an interim final rule at 90 FR 47201). It extends the restrictions that apply to a listed party (on the Entity List, the Military End-User List, or certain Specially Designated Nationals) to any foreign entity that is 50% or more owned, directly or indirectly, individually or in aggregate, by those listed parties. The affiliate is restricted even though it is not, itself, named on any list.
Important and easy to get wrong: the Affiliates Rule was not in force when this was published. BIS stayed it for one year (November 10, 2025 through November 9, 2026) as part of a U.S.–China understanding. The BIS Affiliates Rule is suspended through November 9, 2026 and is scheduled to take effect November 10, 2026 absent further BIS action (BIS final rule, FR 2025-19846, staying the interim final rule at 90 FR 47201). While the stay holds it is not operative under the EAR. Plan for its return.
When it does return, a clean name-against-the-list check stops being sufficient for an export transaction. You have to resolve ownership. BIS paired the rule with a know-your-customer red flag: if you have reason to know a foreign party has a listed owner, you have an affirmative duty to determine the ownership percentage, and if you can't, to seek a license. Because these affiliates are never individually listed, the Consolidated Screening List is expressly not an exhaustive answer.
None of this is conceptually new to anyone who screens for sanctions: OFAC's 50% rule has long treated entities owned 50%+ by blocked persons as blocked. The BIS rule pulls export controls in the same direction, toward ownership analysis.
Where SecurePoint fits: screening records the list version, the result, and the disposition. OFAC 50% ownership results run in shadow mode by default and do not change the access decision. SecurePoint screens names against the BIS Entity List, MEU List and Denied Persons List on every date. A strong possible match is blocked pending review, and a weaker one can be held for documented human review. A reviewer then confirms or rules out the match, and a denial is a separate recorded compliance decision. It does not yet calculate Affiliates Rule ownership, and it does not start blocking automatically when a scheduled date arrives. The legal determination stays with you.
Why one date plus one team is the actual risk
A large prime can absorb two simultaneous regulatory changes with two different departments. The mid-size and small contractors that make up most of the defense industrial base cannot. At those companies, the person chasing a C3PAO assessment slot is frequently the same person who owns vendor screening, visitor access, and the audit file. Two regulatory clocks, one understaffed function, one date.
Treated as two separate fire drills, this is a brutal fall. Treated as one posture (prove who gets access, prove who you do business with, and keep the evidence), it is a single program with two outputs. The contractors who come out ahead will be the ones who stopped seeing “physical security” and “export screening” as different problems months before November.
Two rules, side by side
- Agency
- Department of Defense (32 CFR 170 / DFARS 252.204-7021)
- What was scheduled for Nov 10, 2026
- Third-party C3PAO Level 2 certification as a condition of award for CUI work
- Status
- Phase 2 C3PAO transition suspended (Class Deviation 2026-O0025)
- Control SecurePoint supports
- NIST 800-171 Physical Protection (visitor access evidence, audit trail)
- Agency
- Bureau of Industry and Security (EAR, 90 FR 47201)
- What was scheduled for Nov 10, 2026
- Restrictions extend automatically to 50%+ owned affiliates of listed parties
- Status
- Stayed through November 9, 2026; scheduled to take effect November 10, 2026, not guaranteed
- Control SecurePoint supports
- Ownership-aware screening; OFAC 50% in shadow mode by default; BIS affiliate hits held for review
What to do while Phase 2 is paused
Scope your CUI and keep the self-assessment evidence current. The C3PAO transition is suspended; DFARS 252.204-7012 is not.
Make physical-access evidence audit-ready: visitor logs, escort records, and access decisions mapped to the NIST 800-171 PE controls.
Inventory suppliers and vendors and stand up ownership-resolution screening now; don’t wait to see whether the rule sticks.
Re-screen continuously. Lists and ownership change; a one-time check is not reasonable care.
Keep timestamped records of every screen, access decision, and disposition. Reasonable care is something you prove, not something you assert.
Frequently asked questions
Primary sources
- CMMC Program: 32 CFR Part 170 (Federal Register)
- DFARS 252.204-7021 (Acquisition.gov)
- One-Year Suspension of the Affiliates Rule (Federal Register)
- BIS: Bureau of Industry and Security
- NIST SP 800-171 Rev. 3
- Dept. of War: CMMC Phase II suspension (July 13, 2026)
Effective dates and rule status change. Verify the current status of any rule against the issuing agency before relying on it. This article is educational and is not legal advice.
One posture for both deadlines
Prove who gets access, prove who you do business with, and keep the evidence, in one place. See how SecurePoint USA supports visitor access controls and ownership-aware screening for defense contractors.